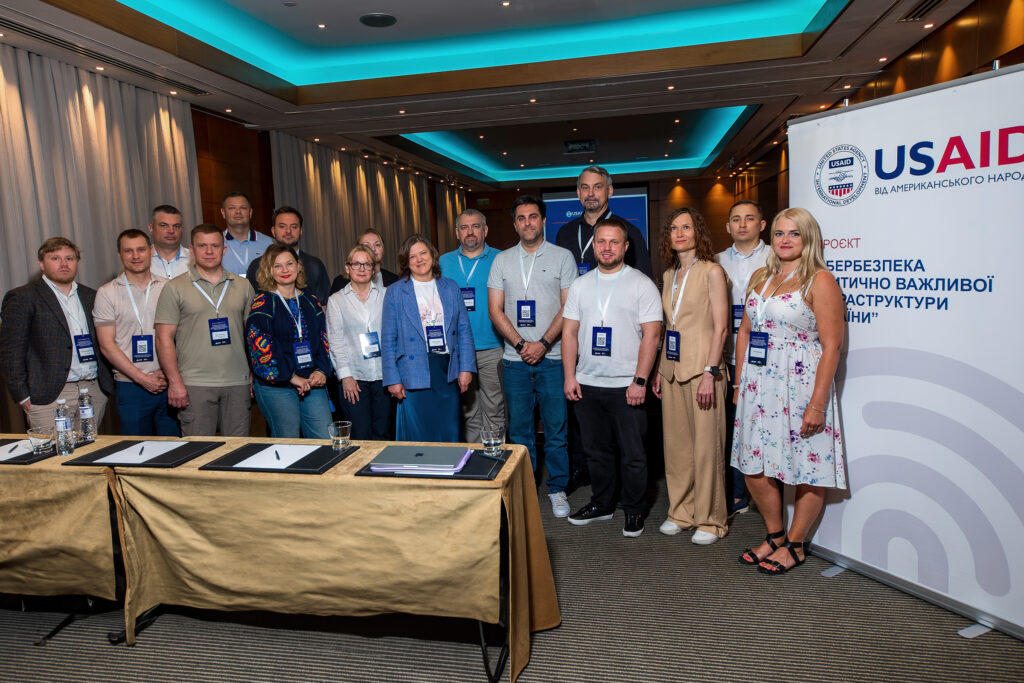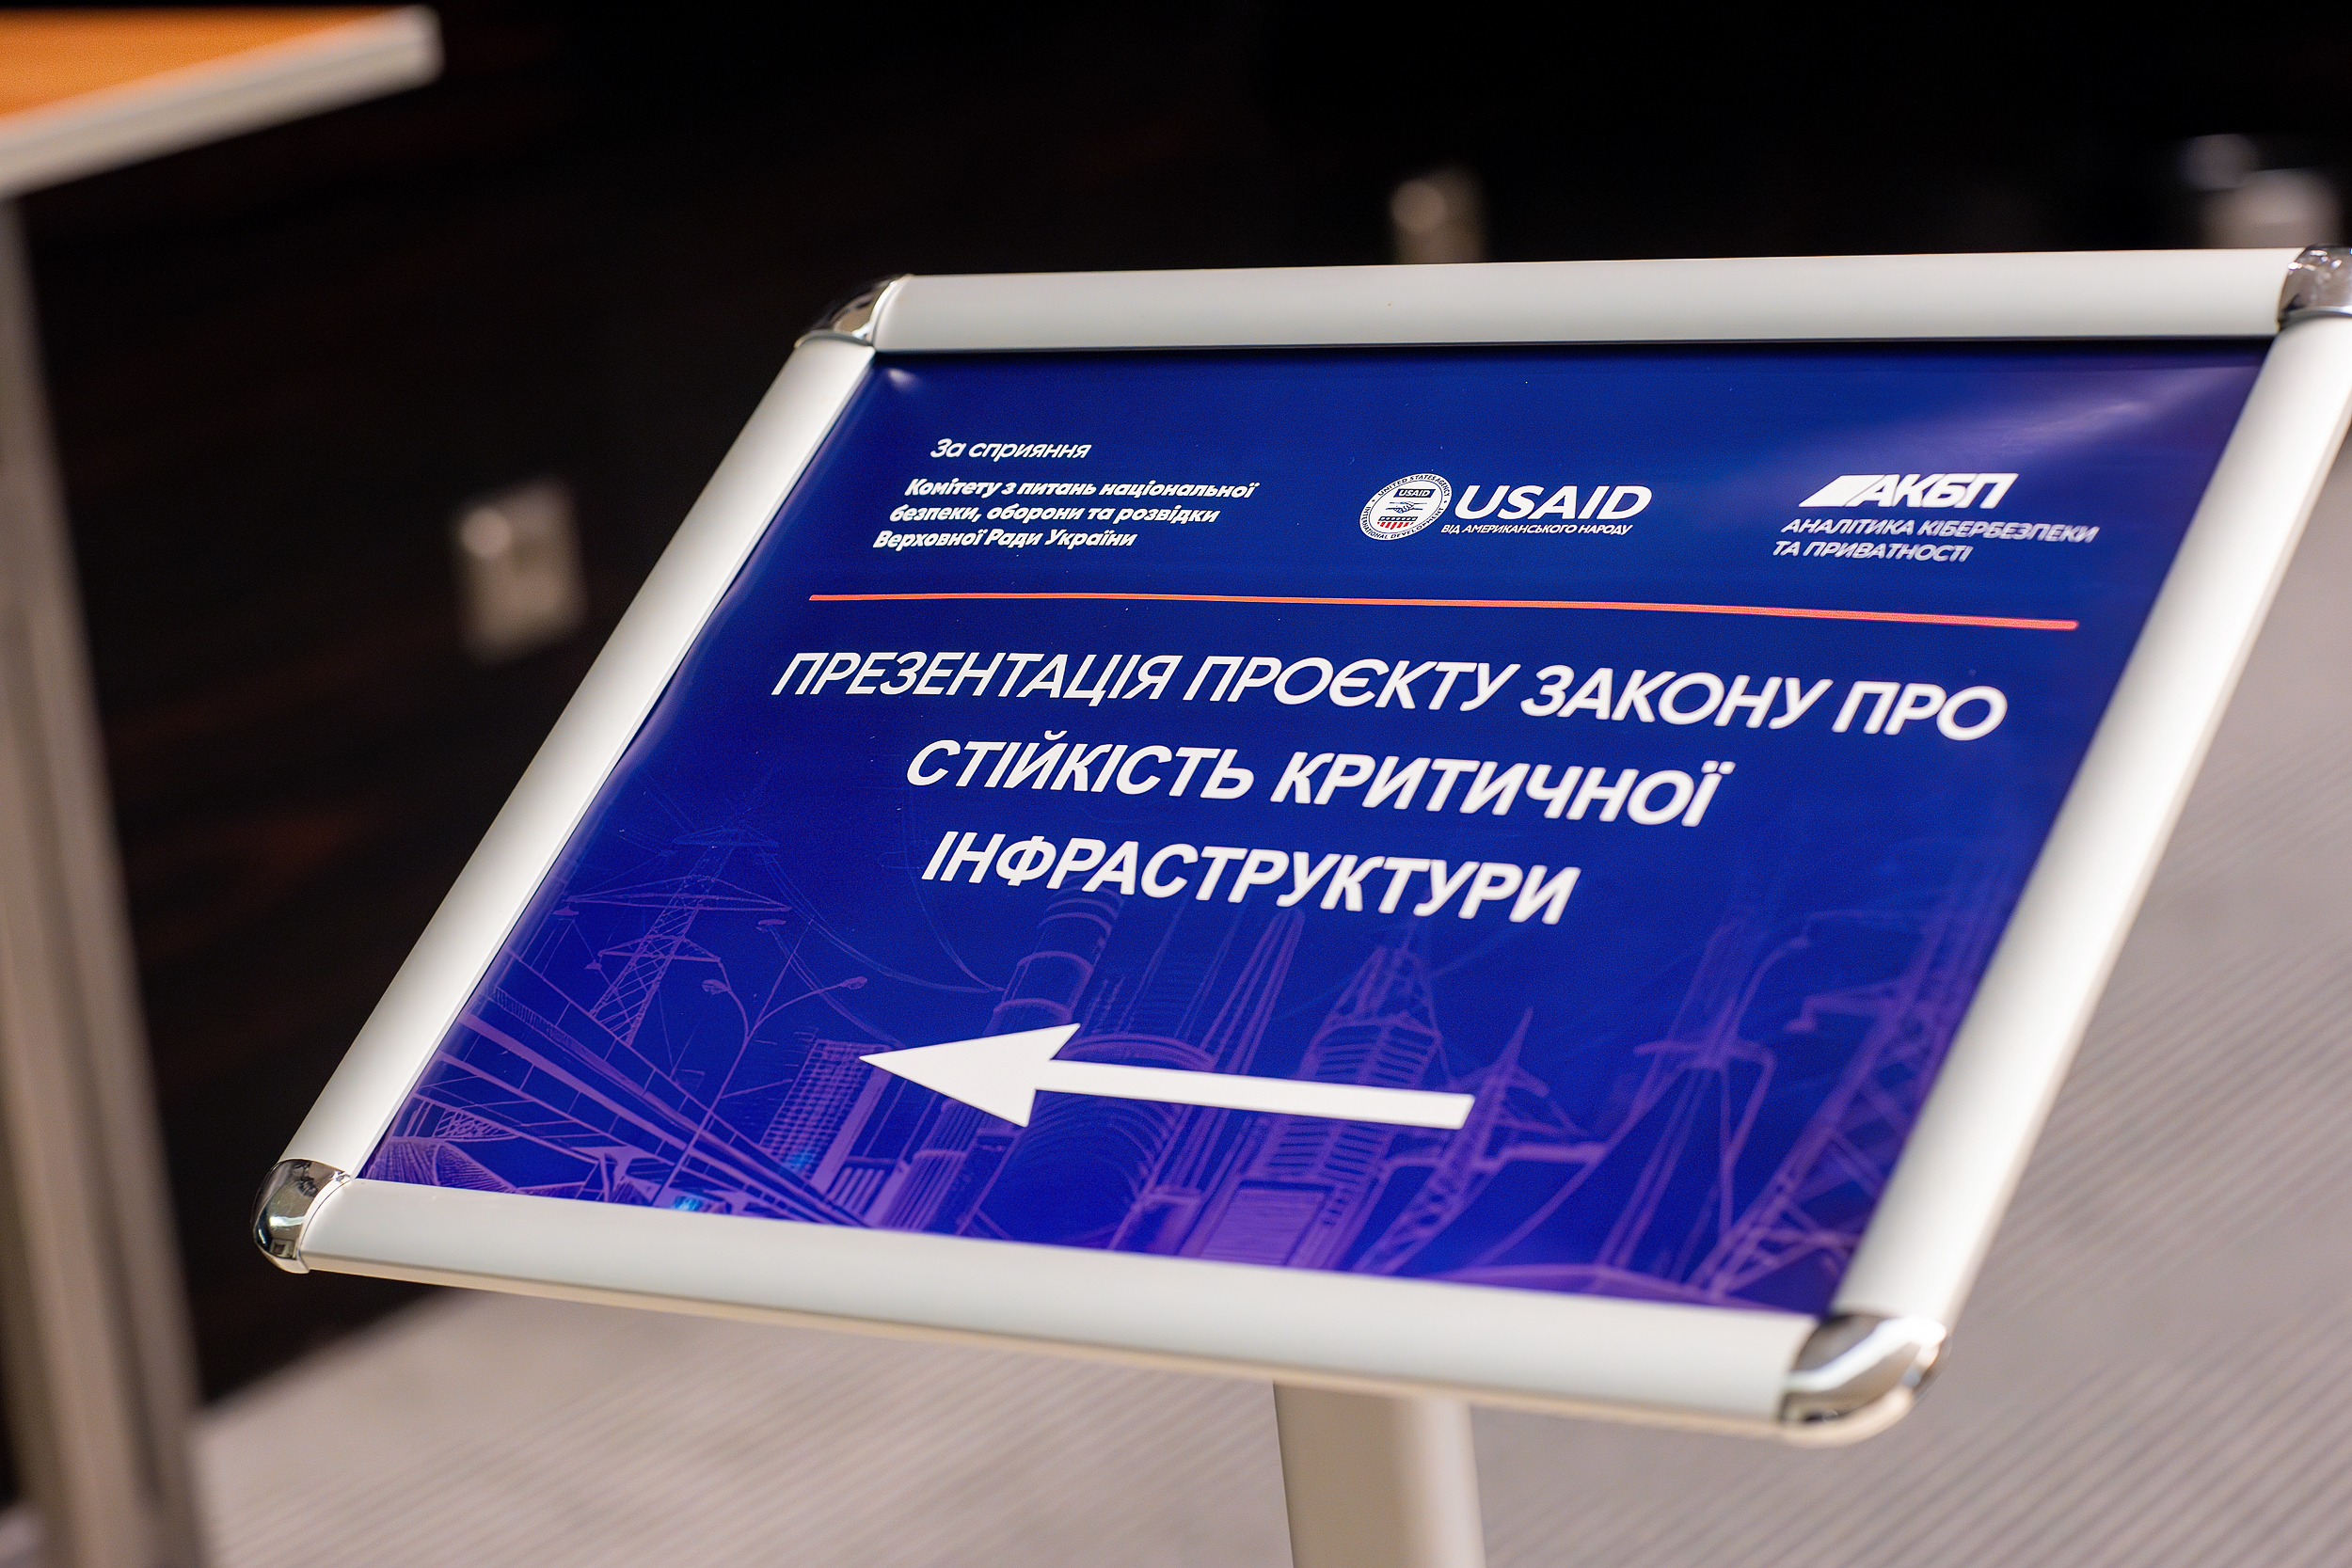
On September 17, "Cybersecurity and Privacy Analytics" LLC held a discussion of the second draft law developed by our team regarding the regulatory and legal settlement of measures for a high level of cybersecurity of Ukraine's digital and other critical infrastructure.
The draft law implements Directive (EU) 2022/2555 on measures for a high common level of cybersecurity (NIS 2 Directive), and is important already now, since electronic trust services and electronic communications services must become an integral part of the EU Single Digital Market, which Ukraine aspires to join even before EU accession.
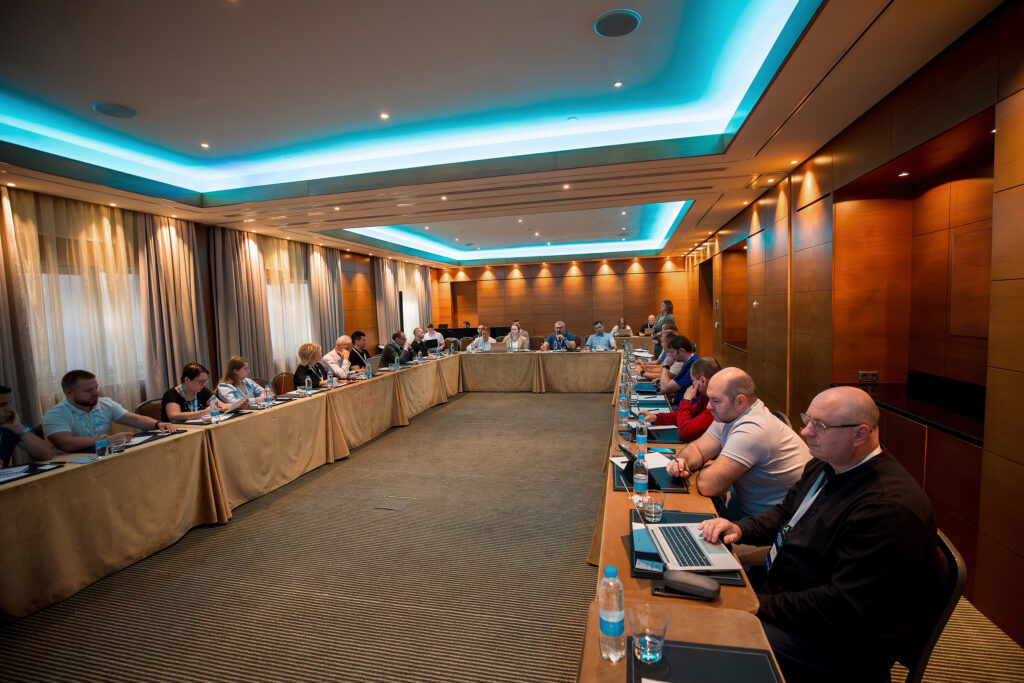
The discussion took place within the framework of the grant activity "Approximation of Ukrainian legislation in the field of critical infrastructure and cybersecurity regulation to EU legislation," carried out by "Cybersecurity and Privacy Analytics" LLC with the support of the USAID Project "Cybersecurity of Ukraine's Critically Important Infrastructure."
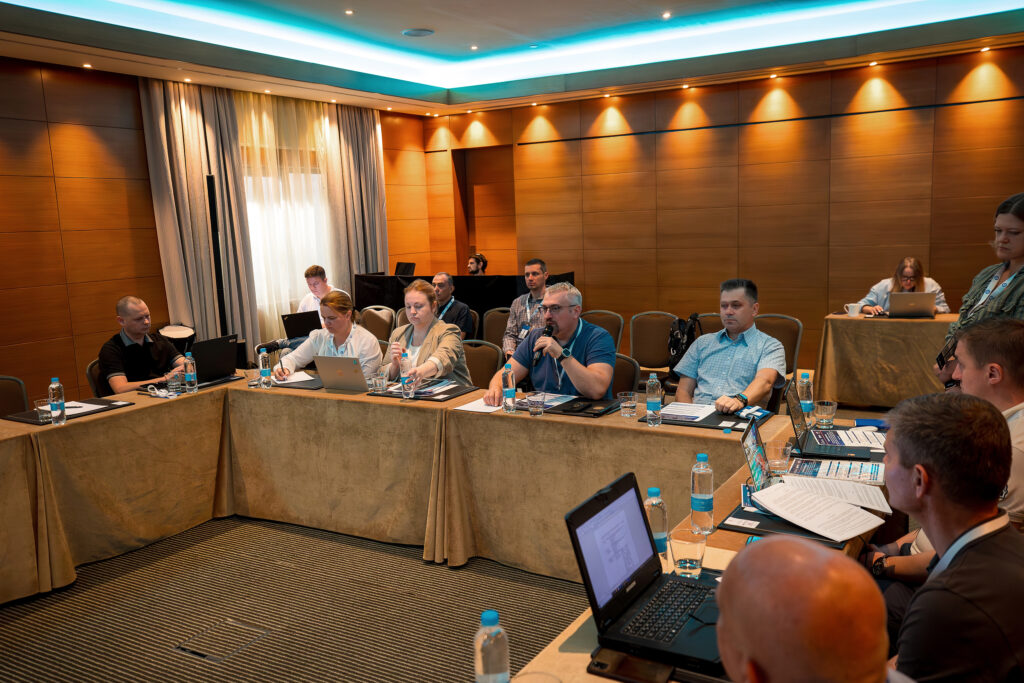
The participants of the discussion, which was also supported by the Verkhovna Rada of Ukraine Committee on National Security, Defence and Intelligence, considered important issues that need to be resolved before submitting this draft law for registration in the Verkhovna Rada of Ukraine.
First of all, these are issues regarding:
- Is it appropriate to restate the Law of Ukraine "On the Basic Principles of Ensuring Cybersecurity of Ukraine" in a new edition?
- The status and powers of the Authorised Body in the field of cybersecurity
- Is it appropriate to recognise the Law of Ukraine "On Protection of Information in Information and Communication Systems" as having lost effect?
- Is reform of the system for confirming the security compliance of the information protection system in information and information-communication systems of public electronic registers necessary – from building a comprehensive information protection system to a certification and conformity assessment system?
- The relationship between cybersecurity requirements and requirements for service providers in the field of cybersecurity
- The procedure for organising state (supervision) control
- The appropriateness of reducing or extending the timeframes for bringing the provisions of the law into effect
- and other no less critical and important issues.
The expert discussion was attended by representatives of: the Verkhovna Rada of Ukraine Committee on National Security, Defence and Intelligence, the National Security and Defence Council, the developers, the authorised body in the field of critical infrastructure protection, regulators, relevant ministries, and operators of digital and other critical infrastructure.
The expert dialogue on the regulatory and legal provision of cybersecurity for digital and other critical infrastructure, in view of the prospect of EU integration, will contribute to the development of a common policy, the development of public-private partnership, and will help to elaborate the necessary changes for building measures for a high level of cybersecurity of critical infrastructure under European regulation.
The results of the discussion, key theses and documents proposed for discussion are available at the link.